
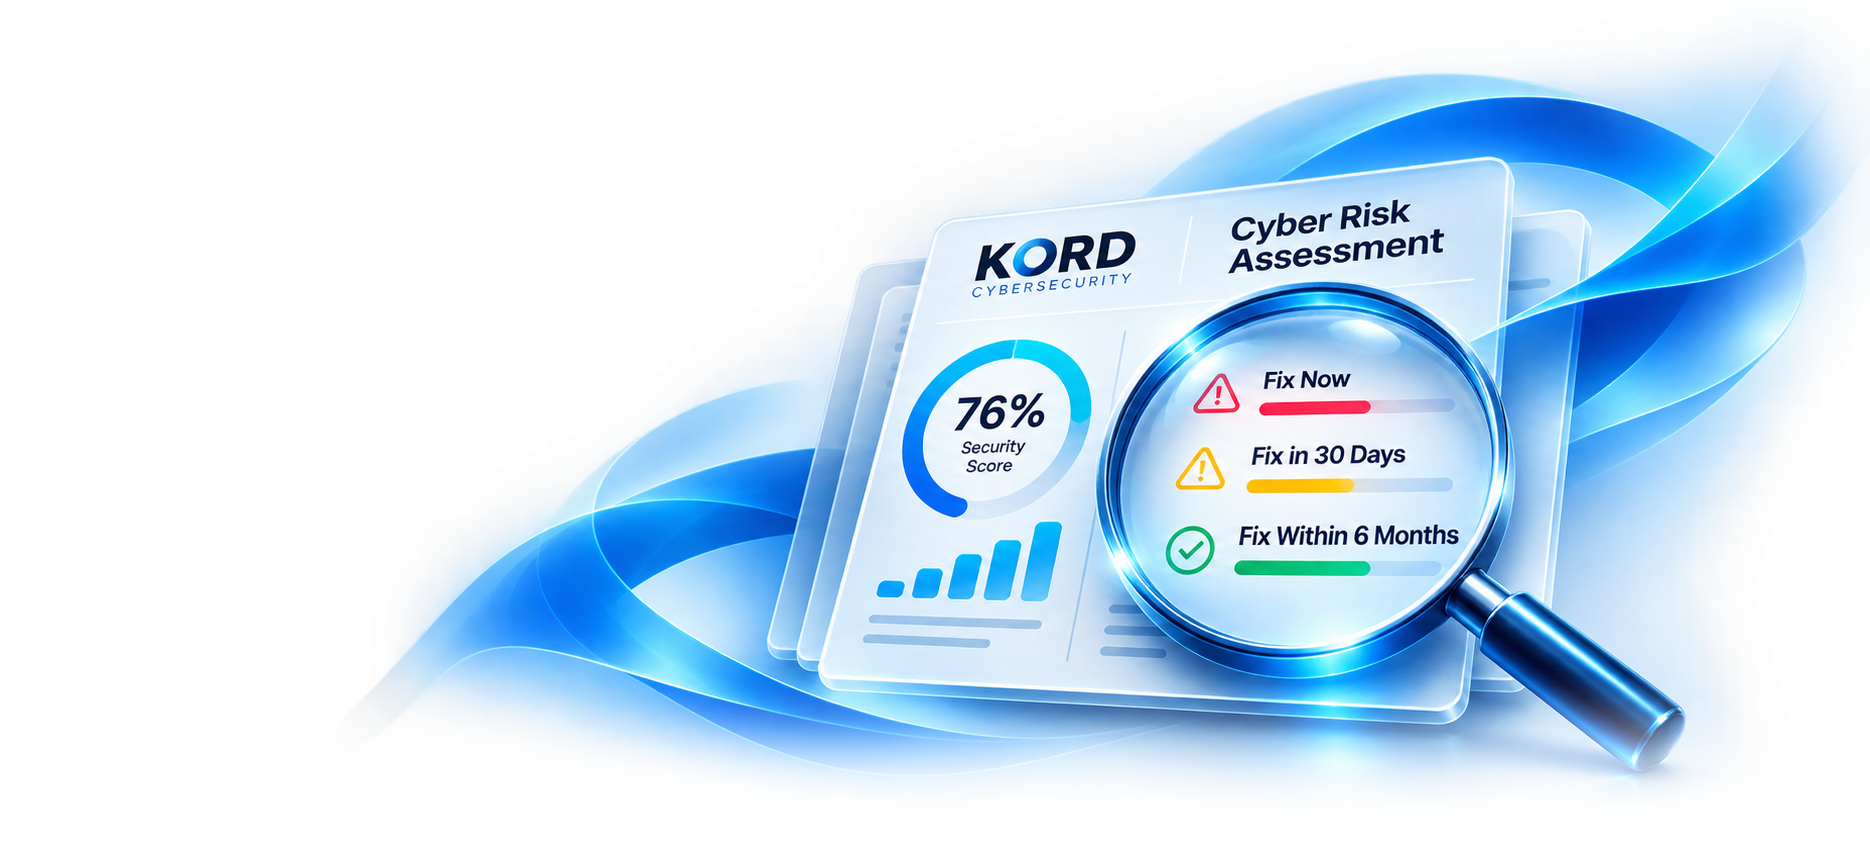
Cyber Risk Assessment
Understand your risk. Know what to fix.
Get an independent picture of your Microsoft 365 security, recent cybersecurity activity and essential AI controls, with a clear, prioritised roadmap for improvement
Actionable recommendations
One-off assessment
Read only review
Understand your exposure
Get a clear baseline of your Microsoft 365 security and see how you compare with similar businesses.
Know what to fix first
Turn technical findings into a practical, prioritised action plan, not another overwhelming report.
Demonstrate good governance
Build evidence to support compliance, insurance, board reporting and client due diligence.
What a Cyber Risk Assessment does
An independent review. A clearer way forward.
We examine your Microsoft 365 setup, security controls and recent activity to show
what is working, where gaps exist and which improvements should come first.
It is a practical, one-off review: you receive the findings and recommendations,
while any changes to your systems remain a separate decision.
Our Assessment Packages
Choose the right depth of review.
A clear baseline for smaller businesses, deeper investigation for more demanding environments, and tailored assessments for complex organisations.
Tier 1
Risk Assessment Lite
For smaller businesses seeking a clear, independent cybersecurity baseline.
US$1,950 / one-off
10 users included + US$5 per additional user
Core Assessment includes
🔹 Business and M365 baseline review
🔹 Cyber Readiness Check and Secure Score
🔹 30-day security activity and score review
🔹 Regional and industry comparison
🔹 Essential AI and security-control checks
🔹 Ranked written recommendations
Tier 2
Risk Assessment Plus
For organisations with more users, sensitive data, or deeper assurance requirements
US$3,250 / one-off
25 users included - US$10 per additional user
Everything in Lite, plus
🔹 90-day tracking and investigation
🔹 Control-by-control industry benchmarking
🔹 BEC, CIS, and ZT benchmark checks
🔹 Expanded AI and data oversharing checks
🔹 SaaS cybersecurity and control gap review
🔹 30-minute guided feedback session
Tier 3
Custom Assessment
For 100+ users, multiple Microsoft 365 tenants, or complex entities and regions
Quote / on request
Scope tailored to your environment
Assessment may include
🔹 Plus assessment adapted to your scale
🔹 Additional Microsoft 365 environments
🔹 Multiple business entities or regions
🔹 Optional executive / board briefing
🔹 Agreed scope and quotation from day one
All prices are in US dollars and represent one-off assessment fees. Additional users are charged at the rate shown. Client-owned software licences remain separate.
Package Details
Explore what’s included.
Both packages establish a cybersecurity baseline and provide clear recommendations. Plus adds greater depth, expanded AI and SaaS checks, and a guided conversation.
For larger, multi-tenant or multi-region environments, we'll agree a custom scope.
-
Establish your baseline - Questionnaire, staff self-assessment, joiner/leaver review, user and domain inventory.
Review recent activity - 30-day analysis of mail flow, URL protection, malware/spoofing, compromised accounts and web filtering.
Prioritise the response - Written recommendations grouped into Fix Now, Fix in 30 Days and Fix Within 6 Months.
Measure readiness - Kord Cyber Readiness Check, Microsoft Secure Score, 30-day score tracking and regional / industry comparison.
Review core controls - Microsoft 365 security configuration and essential AI-security settings.
-
Everything included in Risk Assessment Lite - Receive the complete foundational assessment, including your cybersecurity baseline, Microsoft 365 configuration review, Secure Score analysis, essential AI security checks and prioritised recommendations.
Expanded 90-day security analysis - We extend the review of your cybersecurity activity and historical security performance from 30 to 90 days, investigating unusual events, emerging patterns and potential warning signs.
Detailed industry benchmarking - Go beyond an overall security score with a control-by-control comparison against available regional and industry benchmarks, identifying where your security measures fall behind comparable organisations.
Independent security standards validation - We assess your environment against recognised benchmarks, including business email compromise (BEC) resilience, the CIS Microsoft 365 Foundations Benchmark and Zero Trust principles.
Enhanced AI and Copilot security checks - A more detailed assessment of the settings, permissions and policies governing how AI tools interact with your business information, including checks for sensitive data that may be shared too widely.
SaaS application security review - Identify third-party cloud applications connected to your Microsoft 365 environment, review their access permissions and highlight potentially risky, unused or unauthorised connections.
Identification of technical control gaps - Receive a detailed breakdown of missing, outdated or incorrectly configured security controls, together with practical recommendations that your internal IT team or external provider can implement.
30-minute guided feedback session - Meet virtually with a Kord cybersecurity professional to review the most significant findings, ask questions and understand the recommended next steps.
Clear guidance for remediation - We'll explain which improvements should take priority and how they can be addressed, helping your business move forward with confidence.
-
Everything in Risk Assessment Plus - Build on the comprehensive analysis, technical security reviews, external benchmarking and guided feedback provided through our Plus package.
Tailored assessment scope - For organisations with more than 100 users, multiple Microsoft 365 tenants, several business entities or operations across different regions, we'll develop an assessment scope appropriate to your environment.
Multiple Microsoft 365 environments - We can extend the assessment across additional Microsoft 365 tenants, providing a more complete understanding of security risks and configuration differences throughout your organisation.
Executive and board-level briefings - An optional executive briefing can be arranged to present key cybersecurity findings, business risks and recommended priorities directly to senior leadership or other stakeholders.
Custom recommendations and next steps - Receive findings and practical recommendations aligned with the scale, complexity and security requirements of your organisation.
Pricing tailored to your requirements - We'll agree the scope of your assessment and provide a quotation based on your organisation's environment and needs.
Please note: All Cyber Risk Assessments are carried out on a read-only basis. We review your environment and provide recommendations, but do not modify your security settings unless separately engaged to do so.
The Outcome
You'll receive a business-friendly summary of your cybersecurity position, relevant benchmarks, recent activity and a written action plan.
Rather than leaving you with a long list of technical issues, Kord ranks the recommendations so you can decide what to tackle first.
A report built for action, not just information.
Your prioritised recommendations
Fix now
Highest-priority actions
Fix within 30 days
Next-priority improvements
Fix within 6 months
Longer-term improvements
The Process
How it works.
A straightforward assessment, from confirming your scope to identifying your next steps.
Scope & Quote
We confirm your user count, environments and the package that fits.
Onboard
Complete a questionnaire and provide secure read-only access.
Assess
We examine controls and 30 or 90 days of available activity.
Report
Receive a plain-English baseline, benchmarks and recommendations.
Next Steps
Plus includes a feedback call; Lite can add one if needed.
Working with Kord
Independent insight. No changes without your say-so.
Our assessment uses read-only access to review your environment and report what we find. We don't change your security settings as part of the assessment.
You can act on the recommendations through your own team, your existing IT provider or Kord's separately quoted remediation support. The choice remains with you.
Additional Services
Optional support, when you need it.
Choose additional expertise, validation or practical support only where it adds value to your assessment.
Guided feedback
US$250 / 30 min
An expert walkthrough of the Lite report. Included in Plus.
Executive briefing
US$500 / session
A concise findings presentation for directors, boards or investors.
Remediation support
US$300 / hour
Hands-on fixes or a separately quoted Cybersecurity Project.
Cyber Essentials check
US$750
Check readiness against Cyber Essentials requirements.
Penetration testing
Quote on request
Independent third-party testing, scoped and priced separately.
Follow-up assessment
50% of original fee
Repeat the checks within six months to measure improvement.
Additional M365 tenant
50% of package fee
Include another Microsoft 365 environment in the review.
Optional add-ons are separately priced. Independent penetration testing is delivered by an external third-party provider. The guided feedback session is already included in Plus.
Additional Services
Optional support, when you need it.
Choose additional expertise, validation or practical support only where it adds value to your assessment.
Cybersecurity.
Maintain and improve your protections with ongoing oversight and reporting.
Certifications.
Use identified gaps to prepare for Cyber Essentials or other standards.
Projects.
Scope practical work to address larger remediation or security uplift needs.
50% Credit.
Continue into Managed Cybersecurity: if you sign up within 60 days of receiving your assessment report, 50% of the assessment fee is credited against your first three months of service.
Common Questions
Things to know before you enquire.
Will you change anything in our systems?
No. The assessment is read-only. Kord reviews and reports on your environment; any implementation or remediation is separately agreed
Does Lite include a feedback call?
Lite includes a written report. A 30-minute guided session is available as an add-on; Plus already includes one.
Is this an ongoing subscription?
No. Both Lite and Plus have one-off fees, with additional users and optional services priced separately.
Can Kord help us implement the fixes?
Yes. Remediation support is available by the hour or as a separately scoped Cybersecurity Project.
Talk To Kord
Find out where you stand. Get a clear next step.
Tell us a little about your organisation, Microsoft 365 environment and assessment needs. We'll help scope the right package and provide a quote.